Appearance
Roles And Permissions
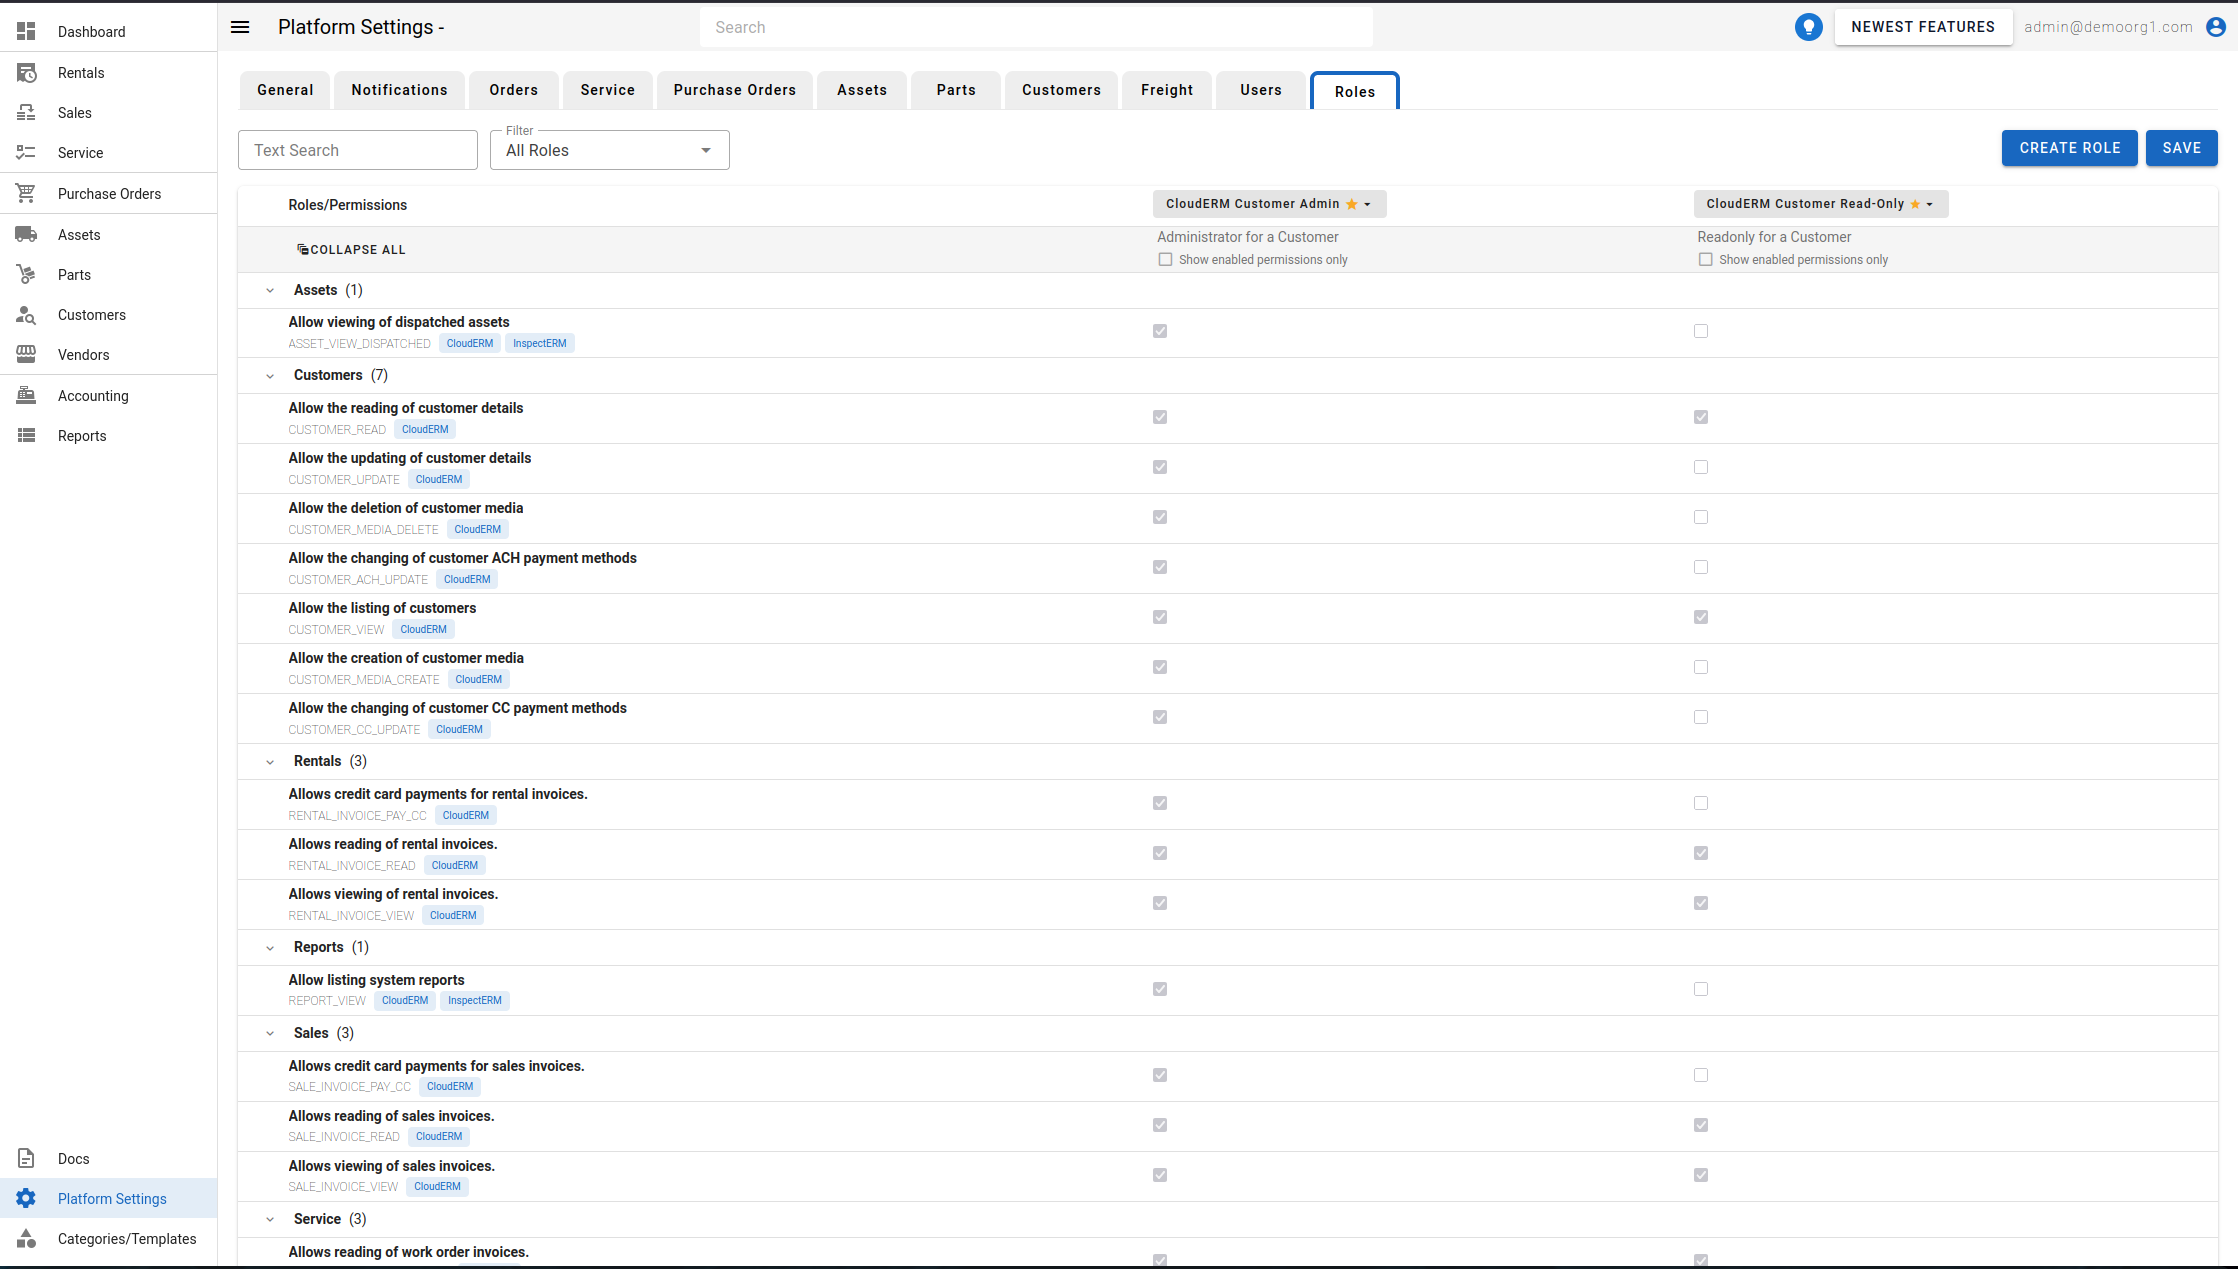
The Roles Page features a table that lists down all permission available on ERM, categorized by their type/domain. To see permissions within a type, simply click on the type's header to expand the row and view it's permissions. Alternately, you can click on the Expand All button to view all permissions.
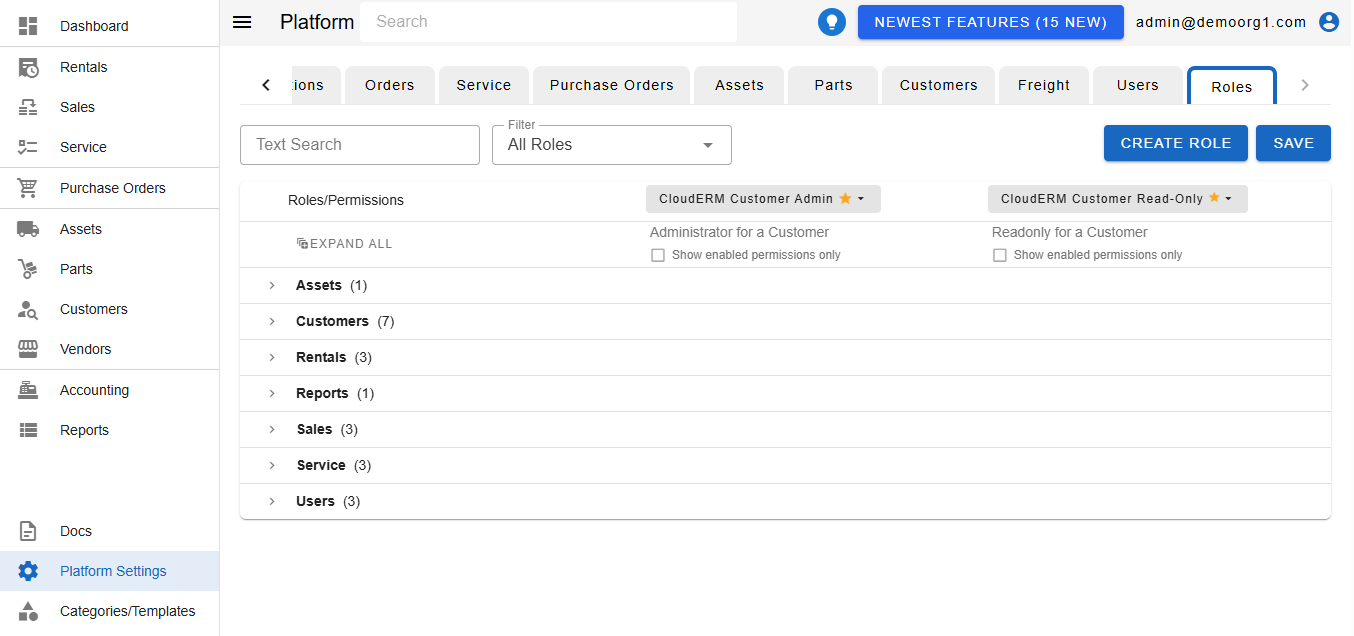
The table allows viewing roles via dropdown in the table header. Roles with a star indicate that the role is default, and cannot be edited. Roles with a shield badge indicate that the role is an org role. Permissions with a shield badge indicate that the permission is an org-only permission , and cannot be set on non-org roles. To see all available roles, simply click on one of the two dropdown in the table header to see the complete list of roles.
Permissions also display a module tag showing which module each permission belongs to — a Tier Module chip for permissions in a subscription-tier module, or an Add-On Module chip for permissions in an optional add-on module. Permissions that belong to a module your organization does not have enabled are not available to assign.
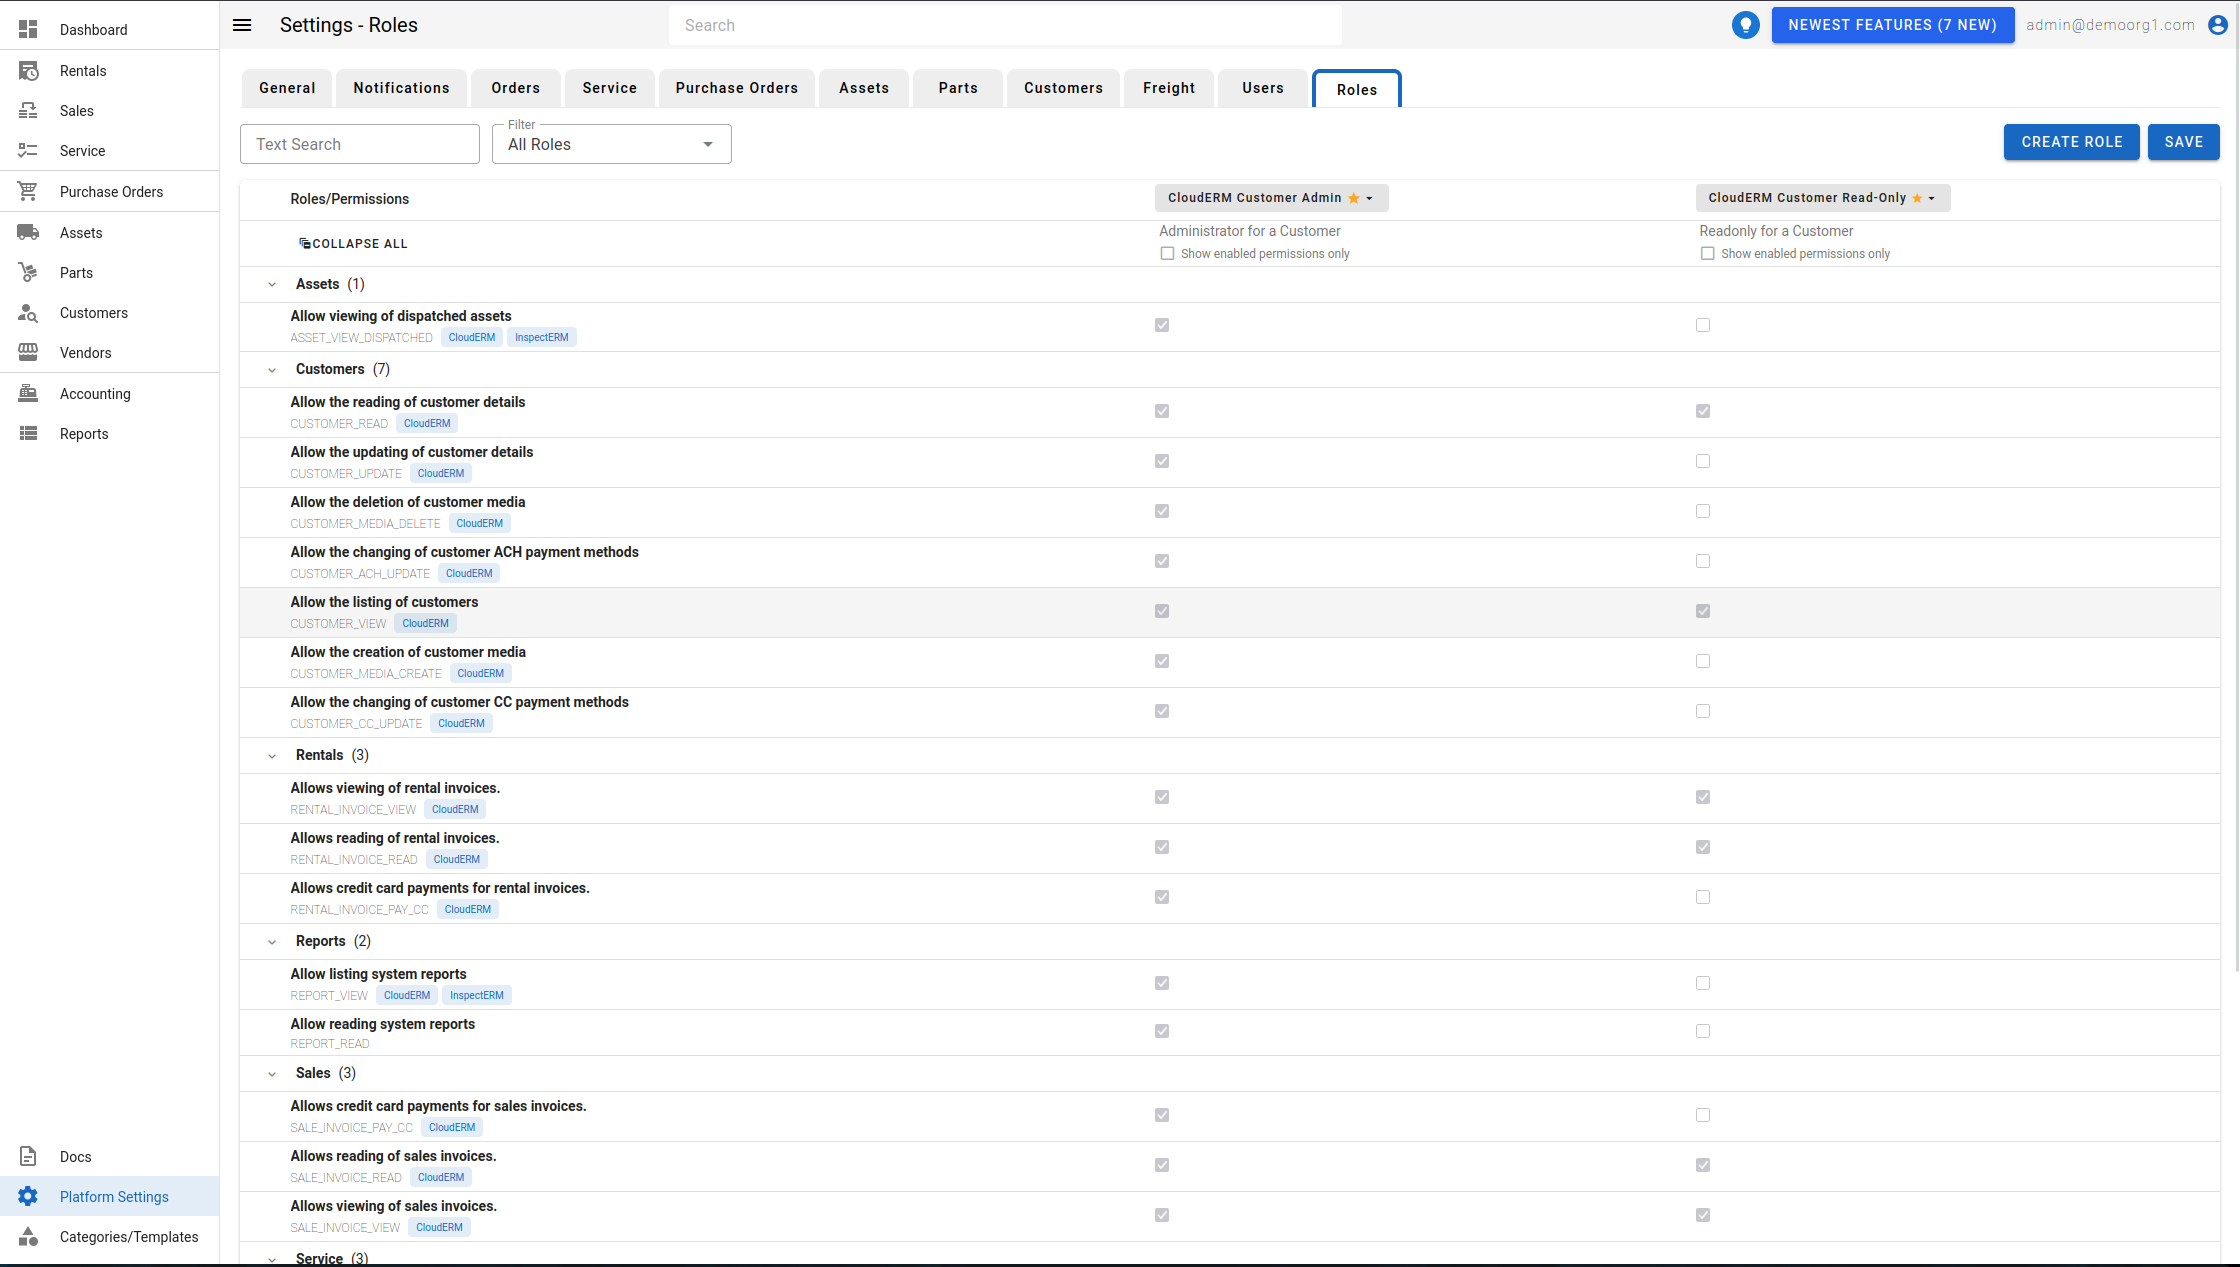
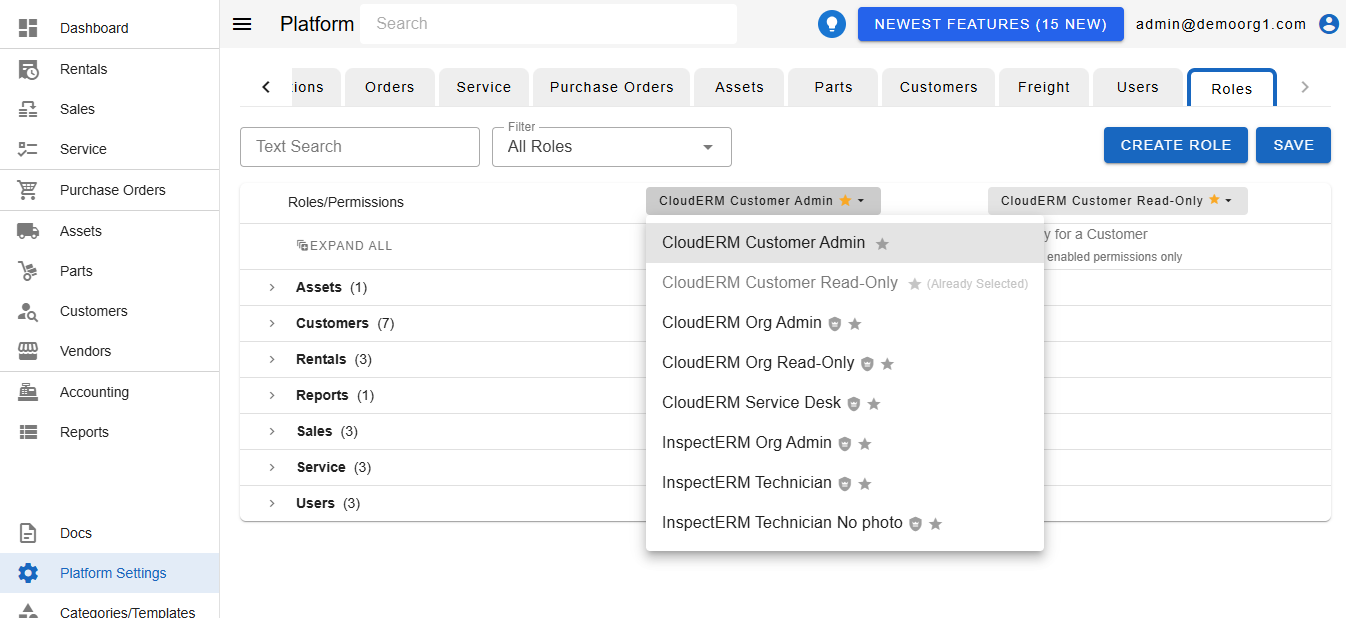
Atop the role-permissions table is a single filter that can be used to filter what type of roles are shown in the dropdown. To only see permission enabled for a certain role, select the role via one of the two roles dropdowns and the check the Show enabled permissions only checkbox for that role
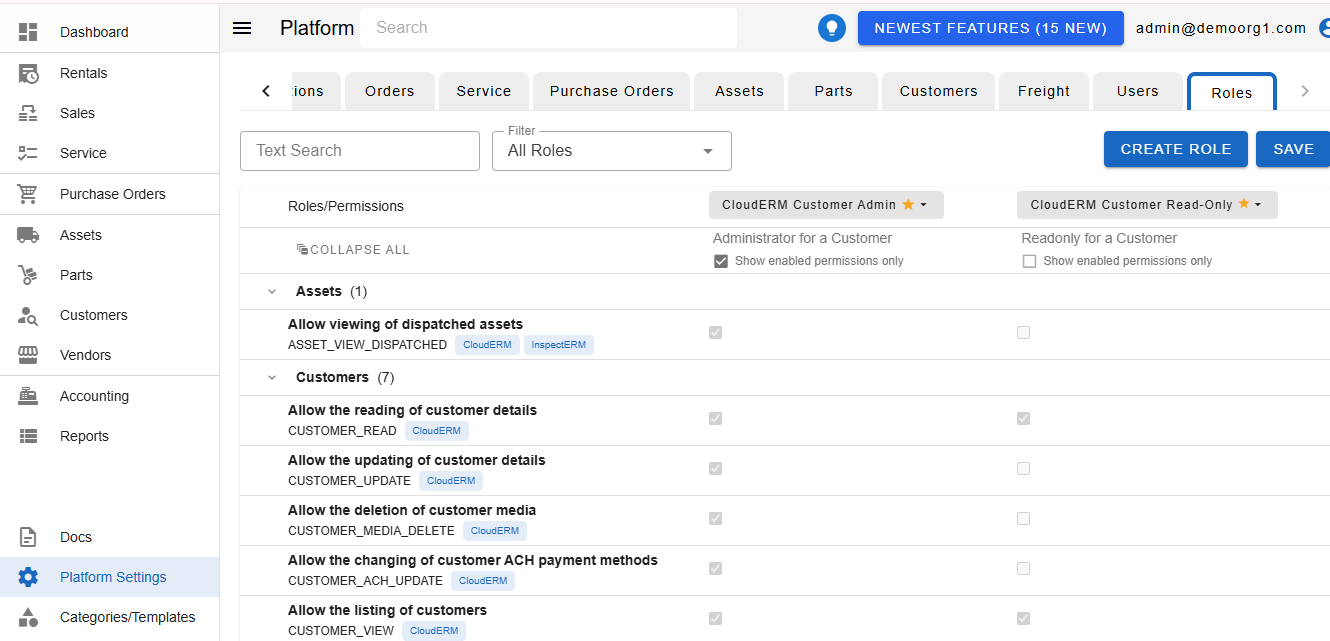
The table allows modifying permissions for roles. To modify a role's permissions, click on one of the two dropdown in the table header and select your desired role. Then toggle any permissions you wish to change and click the Save button to sync the update permissions on the server.
The table allows modifying two roles at once, for better efficiency, visibility and ease of comparison.
When a customer (portal) user manages roles, only that customer's own custom roles are editable. The shared default customer roles stay read-only, and saving updates only the editable roles.
Creating a New Role
To create a new role, click on the Create Role button to open the New Role Popup.
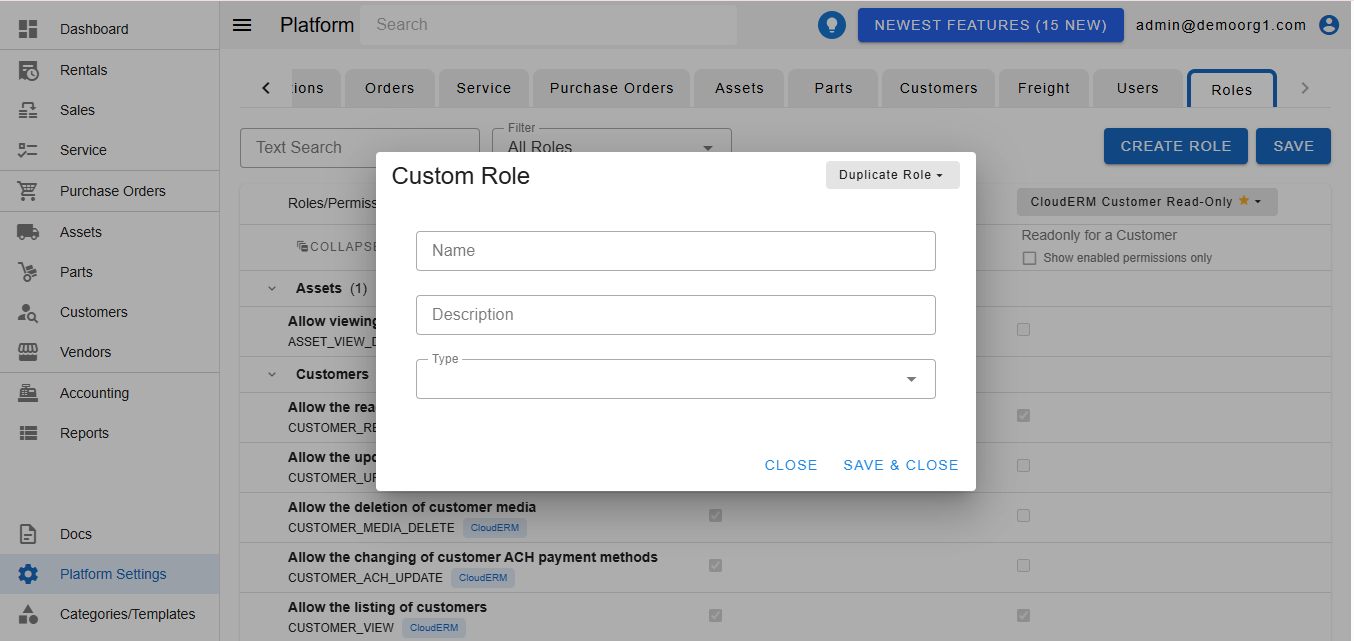
Fill in the resultant form and click the Save button to sync the new role on the server.
Duplicating Roles
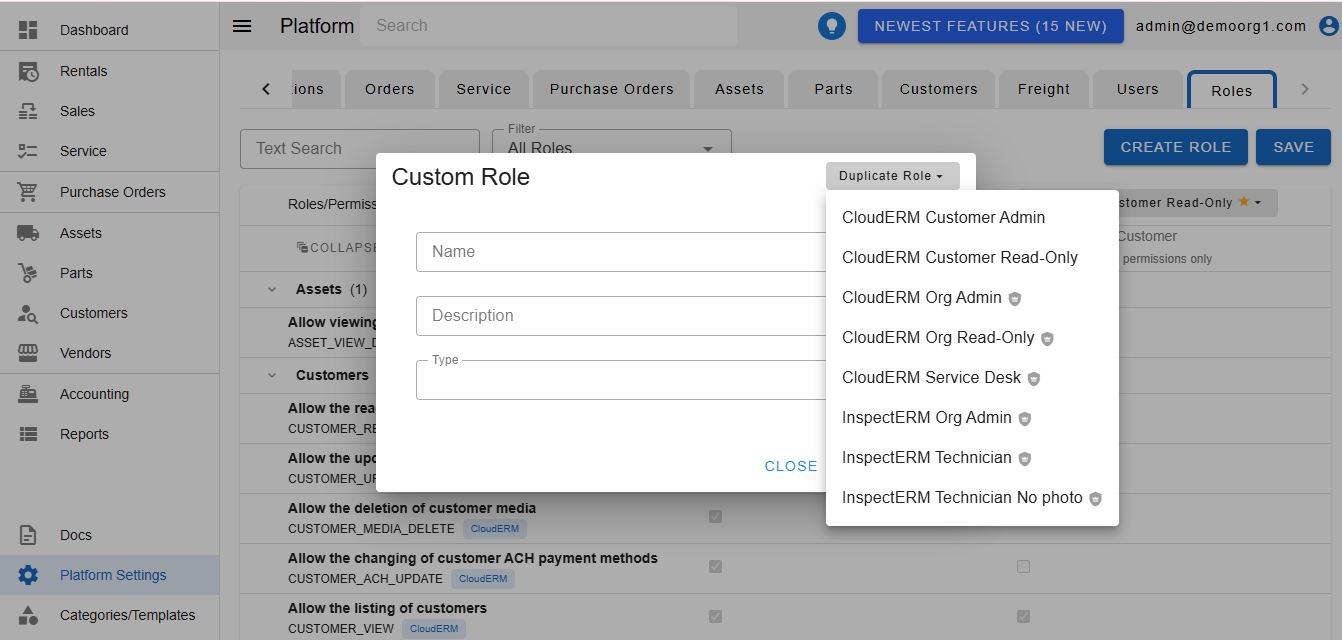
To duplicate a default role, click on the Duplicate Role dropdown visible on the top right corner of the New Role Popup. Select a default role from the resultant dropdown. This will pre-fill details from the default role in the popup's fields. Click Save to duplicate the role
Default roles cannot be modified or deleted. Custom Roles show additional buttons adjacent to the dropdown, that can be used for editing or deleting the role.
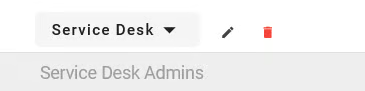
To edit a role's name, click the pencil icon adjacent to the dropdown. This opens the New Role Popup pre-filled with the role's details.
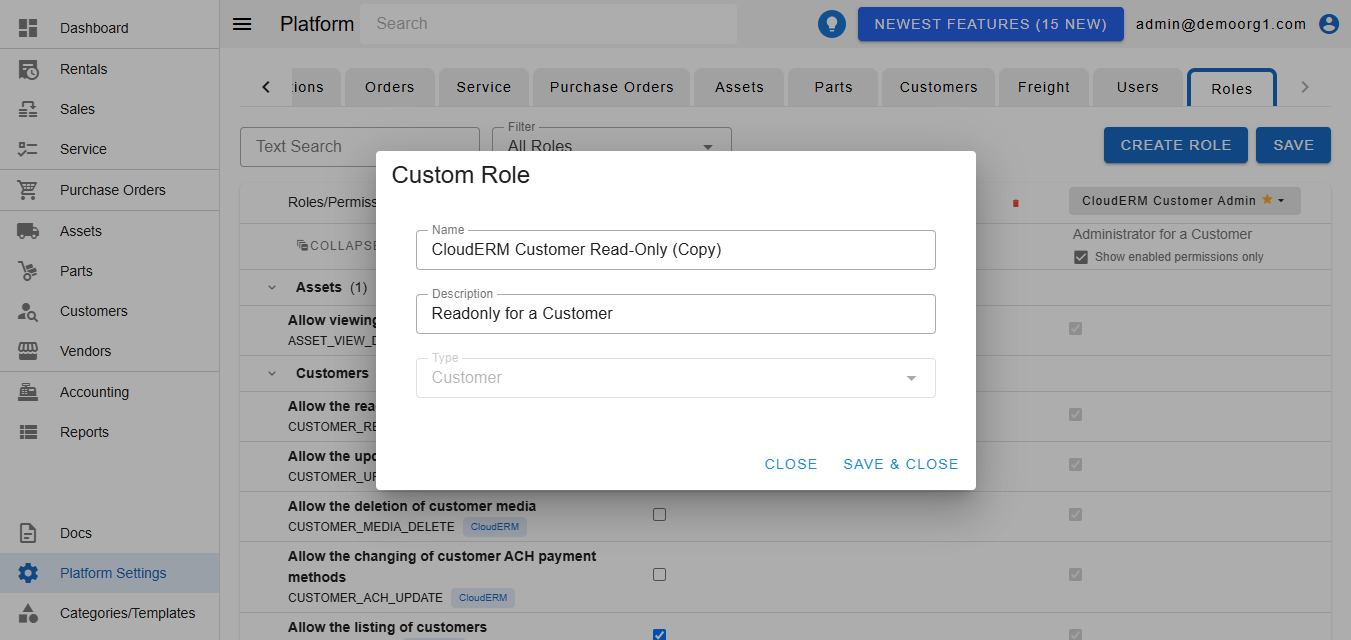
Modify the role's name (or any other field) and click Save to update the role.
To delete a custom role, click on the trash can icon. The user will be prompted with a confirmation dialog. The user can choose to proceed with the deletion, or abort.
The delete button will appear greyed out and disabled for custom roles that are currently assigned to users.
Examples of permission-gated behavior
Permissions control what each role can see and do throughout CloudERM. Some notable examples:
- Reports are gated per category — a role needs the general report-access permission plus the category permission (Accounting, Assets, Customers, Service, Sales, or Daily Summary) to see reports in that category. See Viewing and Generating Reports.
- The Accounting menu and Accounts Receivable area appear only for roles with cash-drawer or GL-configuration access, or with both report-access and the Accounting-reports permission. Customer-scoped (InspectERM) users never see them.
- Dashboard widgets are gated individually — each widget (Active Assets, On Order Assets, On Order Parts, Invoices, Unassigned & Past Due Work, and My Pending Assets) has its own permission.
- Taking payments and deposits requires a payment-posting permission — without it, the Take Deposit and balance-payment controls are hidden.
- Overriding a customer's credit limit: a role with the credit-limit-override permission can acknowledge and proceed past a credit-limit block when promoting an order or posting a payment; other roles are hard-blocked.
- Editing orders after they leave the quote stage is permission-gated: editing an open sales order, editing a closed rental contract (with a separate permission when the invoice has already been sent), and editing a purchase order at its released/received/closed states each require their own permission.
- Invoice Delivery Settings (see Invoices settings) require the invoice-delivery-settings permission and are available to CloudERM organizations only.
- User notification preferences (see User Profile) are gated per area — Rentals, Invoicing, Service, Sale, and System — each with its own "Allows User To Enable ... Notifications For Themselves" permission. A user can only switch on their own email notifications for an area if a role grants that area's permission; without it, the notification's toggle stays visible but disabled. The Rentals, Invoicing, and Sale notification permissions are available to CloudERM organizations only. Note that inspection notifications are gated by the business area they concern rather than by where they're grouped in the table — dispatch/off-rent inspections and sale inspections are gated by the Rentals and Sale permissions respectively, even though both display under the Service section.